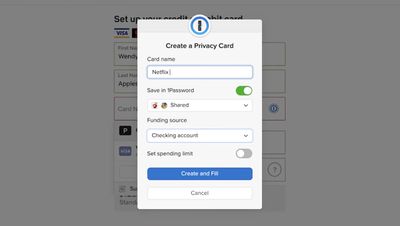
1Password today announced a new partnership with Privacy.com, allowing users to make safer payments online by creating virtual cards that are unique to each of your online accounts.
1Password users can do this in their browser, and soon the feature will launch as a Safari extension. Each virtual card is locked to a particular merchant, and can only be used for that site or service. This way, if the card details are ever exposed in a data breach, it can't be used elsewhere.
When asked to enter a card number for an account like Netflix or Hulu, 1Password will present an option to create a virtual card instead. The virtual card will funnel payments from an existing credit or debit card, or banking account.
Users can set spending limits, set it as a one-off payment or monthly/yearly payment, and more. The card can be saved in 1Password for easy access, and when you go to enter payment again, 1Password will prompt users with their existing virtual cards.
The feature is limited to users in the United States for now. 1Password is also running a promo that takes 25 percent off your first year of 1Password -- including Business, Teams, and Families -- for a limited time.
Note: MacRumors is an affiliate partner with 1Password. When you click a link and make a purchase, we may receive a small payment, which helps us keep the site running.
One of my credit cards offered this about 10 years ago, then stopped offering the feature without explanation. Honestly, I’ve missed it ever since — no idea why it was discontinued.
I can tell you why card issuers stopped doing this; nearly every step of the payment path makes money on fraud, so their intent is to make it sound like they want to stop fraud, while really wanting it to continue. They also derive no financial benefit from the overhead of developing and supporting a one time card technology; i.e. doesn't help the bottom line or stock price if their customers are getting ripped off.
Here's how it works. Criminal obtains a stolen card and places an order on website XYZ. That website uses a payment processor, who is responsible for taking the card from website software to payment network, and possibly doing things like address validation, CVV check, etc. They charge a transaction fee for this, perhaps 5 to 25 cents depending on volume. Maybe the website owner has some add-on services like "anti-fraud" filters, which add an additional few cents to the transaction fee. Typically, if the transaction had been declined because it was a one time use credit card that was no longer valid, the fee would not be assessed. So, first entity involved would lose money by stopping fraud.
Moving on; fraudulent charge is allowed to go through. Now the payment network gets a taste; this would be larger behind the scenes entities. They'll make a small percentage on the transaction.
Finally, the business owner's merchant account, the card issuer, and Visa/MC all get their taste. You'll typically pay the largest of the fees to your merchant account, the one who's handling the actual moving of money. They'll take a couple percent; perhaps less than 2% for a large company, or as much as 2.7-4% as a small biz. Now, if the shopper used a rewards card, the card issuer and Visa/MC tack on some additional basis points, because rewards aren't free, the sellers actually pay for your rewards by way of higher fees they can't escape, since they aren't allowed to not accept rewards cards.
Merchant now ships your product if it goes out the door before the cardholder realizes their card has been used. Card holder later realizes the fraud has occurred, disputes the charge.
Here's where it gets even better. The merchant account provider + Visa/MC charge the merchant a fee for the privilege of having been ripped off and having a chargeback. They will immediately deduct the disputed amount from the merchant's account, hit them with a $10-20 or even $30 chargeback fee, and ask for documentation proving the cardholder agreed to the charge, which is of course impossible with internet transactions unless you did some kind of really expensive identity validation where that third party validates and guarantees the identity. So now you've lost your merchandise, you've been charged a fee for getting ripped off, and on top of all that, they still keep the transaction fees. In some cases, they may even keep some portion of the merchant account percentage fee, for money they've taken back; the smaller the business, the less leverage they have over this racket.
There is an exception to the above; Amex doesn't charge the chargeback fee, nor do they typically take the money away during the dispute. They open an 'inquiry' and you only lose the money when you can't demonstrate the cardholder agreed to the charge, but no fee is assessed. Why? Because they charge much higher transaction fees, which is why most businesses hate to accept Amex, but begrudgingly do because it's better than turning away the business. You'll still get hit with the validation and address check fees though, via the party connecting your web store to your Amex merchant account.
I think the only reason Capital One still offers their Chrome browser plugin solution for this is because they realized some people actually care about fraud and perhaps it gives them a competitive advantage given every other card issuer has abandoned the technology. I used to use both BofA and Amex for this but they stopped doing it 5+ years ago, maybe even ten. I ultimately lost access to the Cap One solution because it was tied to my Savor card (restaurant benefits), and given I haven't dined out in six months thanks to covid, when I called to convert to the no-fee version of the card and they said no, I closed the account.
Been using privacy.com for years. It's pretty handy for auto-terminating subscriptions, since you can set an amount and/or time limit on a virtual card.
To anyone that's used both, how does 1password compare to Lastpass ? Better ?
I've gone back and forth a couple times between the two and used each one for at least a year at a time. While there are differences between the two, they both offer the same basic service and I trust each one equally. One big difference is LastPass has a free option where 1Password doesn't. Aside from price, it more comes down to personal preference. There are quite a number of reviews online that compare the two so I suggest googling for those if you want to know specifically what's different between the two.
I currently use 1Password and plan to stick with it. The reasons I switched back is because I prefer their UI and 1Password can be used as a 2FA authenticator for your sites that support 2FA (not sure if Lastpass has added that). The latter makes it really easy to log into sites that use 2FA (e.g. I don't have to go get my phone and open up some authenticator app when I'm trying to log into one of my sites on my computer).
My only options within privacy.com is debt or bank account, no credit card. Like the idea but I also like my points...
Well, that kills privacy.com for me. No way I'm giving up my points.
One of my credit cards offered this about 10 years ago, then stopped offering the feature without explanation. Honestly, I’ve missed it ever since — no idea why it was discontinued.
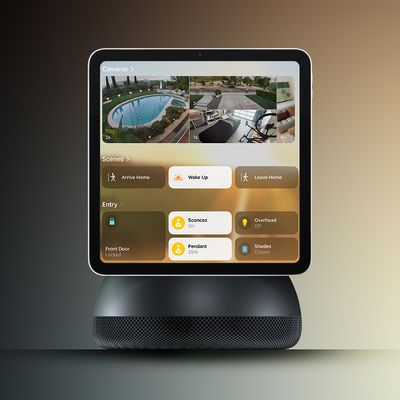
Apple's long-rumored smart home hub will have an iMac G4-style design and a host of unique features, Bloomberg's Mark Gurman reports.
The smart home hub is said to feature a square 6-inch display, with variants that can be placed on a countertop or mounted on a wall. It features a single FaceTime camera on the front, with microphones and speakers in its connected base. Gurman described the...
Apple plans to introduce a series of new smart home products on Tuesday, October 13, according to Bloomberg's Mark Gurman.
Apple reportedly plans to debut its long-awaited smart home hub device, a new HomePod mini, and a new Apple TV on the date. The new HomePod mini and Apple TV are set to retain their existing designs, but tout faster chips to support Siri AI. The new HomePod mini will...
Friday September 25, 2026 8:16 am PDT by Joe Rossignol
MacRumors contributor Aaron Perris has uncovered an image file from Apple for an unreleased Apple TV 4K, suggesting that a new model will finally be released soon. The image is specifically for an "Apple TV 4K (4th generation)" model.
Apple TV 4K (4th generation) image (on a gradient)
The image reveals that the Apple TV will have the same external design as the current model, with all of its...
Apple's first foldable iPhone, with a book-style design featuring a 5.4-inch outer display and a 7.6-inch inner display with a minimal crease down the middle.





Top Rated Comments
Here's how it works. Criminal obtains a stolen card and places an order on website XYZ. That website uses a payment processor, who is responsible for taking the card from website software to payment network, and possibly doing things like address validation, CVV check, etc. They charge a transaction fee for this, perhaps 5 to 25 cents depending on volume. Maybe the website owner has some add-on services like "anti-fraud" filters, which add an additional few cents to the transaction fee. Typically, if the transaction had been declined because it was a one time use credit card that was no longer valid, the fee would not be assessed. So, first entity involved would lose money by stopping fraud.
Moving on; fraudulent charge is allowed to go through. Now the payment network gets a taste; this would be larger behind the scenes entities. They'll make a small percentage on the transaction.
Finally, the business owner's merchant account, the card issuer, and Visa/MC all get their taste. You'll typically pay the largest of the fees to your merchant account, the one who's handling the actual moving of money. They'll take a couple percent; perhaps less than 2% for a large company, or as much as 2.7-4% as a small biz. Now, if the shopper used a rewards card, the card issuer and Visa/MC tack on some additional basis points, because rewards aren't free, the sellers actually pay for your rewards by way of higher fees they can't escape, since they aren't allowed to not accept rewards cards.
Merchant now ships your product if it goes out the door before the cardholder realizes their card has been used. Card holder later realizes the fraud has occurred, disputes the charge.
Here's where it gets even better. The merchant account provider + Visa/MC charge the merchant a fee for the privilege of having been ripped off and having a chargeback. They will immediately deduct the disputed amount from the merchant's account, hit them with a $10-20 or even $30 chargeback fee, and ask for documentation proving the cardholder agreed to the charge, which is of course impossible with internet transactions unless you did some kind of really expensive identity validation where that third party validates and guarantees the identity. So now you've lost your merchandise, you've been charged a fee for getting ripped off, and on top of all that, they still keep the transaction fees. In some cases, they may even keep some portion of the merchant account percentage fee, for money they've taken back; the smaller the business, the less leverage they have over this racket.
There is an exception to the above; Amex doesn't charge the chargeback fee, nor do they typically take the money away during the dispute. They open an 'inquiry' and you only lose the money when you can't demonstrate the cardholder agreed to the charge, but no fee is assessed. Why? Because they charge much higher transaction fees, which is why most businesses hate to accept Amex, but begrudgingly do because it's better than turning away the business. You'll still get hit with the validation and address check fees though, via the party connecting your web store to your Amex merchant account.
I think the only reason Capital One still offers their Chrome browser plugin solution for this is because they realized some people actually care about fraud and perhaps it gives them a competitive advantage given every other card issuer has abandoned the technology. I used to use both BofA and Amex for this but they stopped doing it 5+ years ago, maybe even ten. I ultimately lost access to the Cap One solution because it was tied to my Savor card (restaurant benefits), and given I haven't dined out in six months thanks to covid, when I called to convert to the no-fee version of the card and they said no, I closed the account.
I currently use 1Password and plan to stick with it. The reasons I switched back is because I prefer their UI and 1Password can be used as a 2FA authenticator for your sites that support 2FA (not sure if Lastpass has added that). The latter makes it really easy to log into sites that use 2FA (e.g. I don't have to go get my phone and open up some authenticator app when I'm trying to log into one of my sites on my computer).
Well, that kills privacy.com for me. No way I'm giving up my points.