Apple will be among several U.S. tech giants to attend a meeting at the White House today to discuss cybersecurity and possible security threats posed by open-source software, Reutersreports.
The meeting will be held by U.S. National Security Advisor Jake Sullivan and will focus on "concerns around the security of open-source software and how it can be improved." The meeting was prompted by concerns around a security vulnerability found in open-source software Log4j.
The vulnerability, which posed a threat to organizations that use Log4j around the world, allowed hackers to control a system and remotely execute malicious code.
According to Sullivan, open-source software such as Log4j presents a "key national security concern" as it is often used and maintained by volunteers. Google, IBM, Meta, Microsoft, and Oracle are also expected to attend the meeting.
Note: Due to the political or social nature of the discussion regarding this topic, the discussion thread is located in our Political News forum. All forum members and site visitors are welcome to read and follow the thread, but posting is limited to forum members with at least 100 posts.
Apple has blocked compromised security certificates on its devices that could help attackers impersonate websites, BleepingComputer reports.
The certificates were issued by certificate authority eMudhra. According to Mozilla's investigation, their private keys were all numbers below 256, making them almost instantly recoverable. Attackers could use the affected website certificate keys to...
Wednesday October 28, 2026 10:11 am PDT by Juli Clover
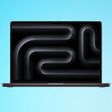
Apple today announced a new high-end MacBook Pro, which is available in 14-inch and 16-inch sizes. The new device has a PROLED XDR display that supports touch gestures, and a glowing rear Apple logo.
Pricing on the MacBook Pro starts at $2,899 for the 14-inch model and $3,399 for the 16-inch model.
Apple says the MacBook Pro has the "world's best display in a pro laptop." The PROLED...
Thursday October 29, 2026 1:47 pm PDT by Joe Rossignol
While the new iPad mini has an OLED display, the device does not support ProMotion, meaning the display's refresh rate is limited to 60Hz instead of 120Hz.
ProMotion support would have allowed for the iPad mini's refresh rate to automatically adjust from 10Hz to 120Hz depending on the content being displayed, but evidently Apple has kept the feature exclusive to the iPad Pro among iPad...
I'm waiting for all the rabbid open-source fans to tell us open-source is much safer than closed-source.
It's not that simple. open-source CAN be safer, it can also be less safe. In open-source, the exact code is out there for anyone to look at. This means anyone could see any flaws and fix them. It also means that anyone could see any flaws and exploit them.
In closed-source, you can't see the code. It's a much different process to exploit the code. Much harder. There are also less people who have access to the code to fix any flaws. So, flaws will stick around longer.
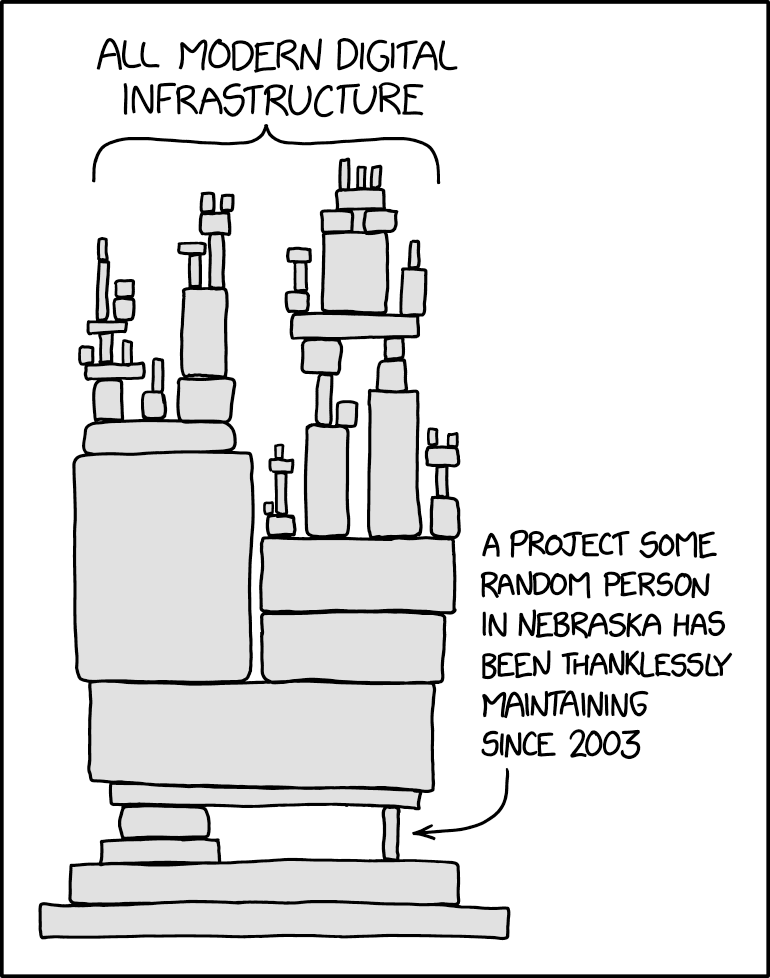
The issue is more that there are a certain amount of core libs that everyone has in their builds. I think now its the Wild West because its no one person/ orgs job to check any of these libs or certify them. … We are leaving for too many core components to be looked after by people for free with no incentive to make sure everything is ok.
The entire Linux community is open source, and yet this is a much more secure platform than Windows has been. And Mac OS and their browsers have heavily benefited from the give and take between Unix and Linux (macOS building on a Unix rather than Linux kernel )
I am almost certain that there have been more security faults in proprietary systems than well maintained open source projects, because the drive behind open source is a more idealistic than the industries “quick to market / milk them all”
With that being said, especially when it comes to web development and the package repositories I see there, I am more doubtful and careful with using and relying on them. I feel it often moves too fast and the community has a different background than e.g. hardcore Linux developers.
I'm waiting for all the rabbit open-source fans to tell us open-source is much safer than closed-source.
It's not that simple. open-source CAN be safer, it can also be less safe. In open-source, the exact code is out there for anyone to look. This means anyone could see any flaws and fix them. It also means that anyone could see any flaws and exploit them.
In closed-source, you can't see the code. It's a much different process to exploit the code. Much harder. There are also less people who have access to the code to fix any flaws. So, flaws will stick around longer.
It's not simple.
Not a rabid open sores fan at all (except back in my teenage years when I went through a rebellious Linux phase ugh), but obscurity does not imply security.