Researchers Discover Vulnerabilities in PGP/GPG Email Encryption Plugins, Users Advised to Avoid for Now - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Researchers Discover Vulnerabilities in PGP/GPG Email Encryption Plugins, Users Advised to Avoid for Now

A warning has been issued by European security researchers about critical vulnerabilities discovered in PGP/GPG and S/MIME email encryption software that could reveal the plaintext of encrypted emails, including encrypted messages sent in the past.
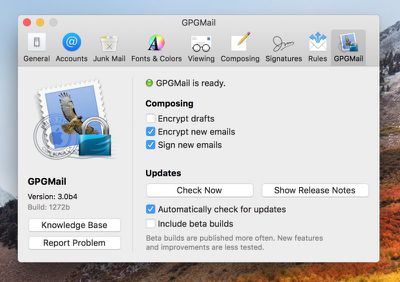
GPGMail pane
The alert was put out late on Sunday night by professor of computer security Sebastian Schinzel. A joint research paper, due to be published tomorrow at 07:00 a.m. UTC (3:00 a.m. Eastern Time, 12:00 am Pacific) promises to offer a thorough explanation of the vulnerabilities, for which there are currently no reliable fixes.


Details remain vague about the so-called "Efail" exploit, but it appears to involve an attack vector on the encryption implementation in the client software as it processes HTML, rather than a vulnerability in the encryption method itself. A blog post published late Sunday night by the Electronic Frontier Foundation said:

"EFF has been in communication with the research team, and can confirm that these vulnerabilities pose an immediate risk to those using these tools for email communication, including the potential exposure of the contents of past messages."

In the meantime, users of PGP/GPG and S/MIME are being advised to immediately disable and/or uninstall tools that automatically decrypt PGP-encrypted email, and seek alternative end-to-end encrypted channels such as Signal to send and receive sensitive content.

Update: The GPGTools/GPGMail team has posted a temporary workaround against the vulnerability, while MacRumors has compiled a separate guide to removing the popular open source plugin for Apple Mail until a fix for the vulnerability is released. Other popular affected clients include Mozilla Thunderbird with Enigmail and Microsoft Outlook with GPG4win. Click the links for EFF's uninstall steps.


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

flyinmac Avatar
109 months ago
Hmm.... security protocol creates a vulnerability. To protect yourself, stop encrypting your emails???

Interesting.
Score: 12 Votes (Like | Disagree)
109 months ago
This looks like another clickbait by (almost pseudo) research teams. The problem is within mail software and not PGP encryption standard or tools.

https://lists.gnupg.org/pipermail/gnupg-users/2018-May/060315.html
Score: 7 Votes (Like | Disagree)
rodpascoe Avatar
109 months ago
Oh the irony.
Score: 6 Votes (Like | Disagree)
flyinmac Avatar
109 months ago
Hope the alert was not sent by email LOL
Going back to using birds to deliver my messages. Considered pigeons... but I want a bird that can shred anyone who tries to intercept my message. Decided on Hawks.
Score: 4 Votes (Like | Disagree)
belvdr Avatar
109 months ago
From what I've read, it's a bug in PGP, not mail
It's a problem in the mail user agent (MUA), not PGP/GPG. From the mailing list:

https://lists.gnupg.org/pipermail/gnupg-users/2018-May/060315.html


The topic of that paper is that HTML is used as a back channel to create an oracle for modified encrypted mails. It is long known that HTML mails and in particular external links like <img href="tla.org/TAG"/> are evil if the MUA actually honors them (which many meanwhile seem to do again; see all these newsletters). Due to broken MIME parsers a bunch of MUAs seem to concatenate decrypted HTML mime parts which makes it easy to plant such HTML snippets.

There are two ways to mitigate this attack

- Don't use HTML mails. Or if you really need to read them use a
proper MIME parser and disallow any access to external links.

- Use authenticated encryption.
It also appears that some versions of OpenPGP already use authenticated encryption. From what I'm reading, this is a really old bug that many wanted to get fixed, but the MUAs fail to fix it.
Score: 3 Votes (Like | Disagree)
Detektiv-Pinky Avatar
109 months ago

<snip>
From what I've read, it's a bug in PGP, not mail
I heard differently. It is supposedly a bug affecting any kind of Email encryption using MIME and automatically loading remote content. Also the in-build S/MIME encryption is at risk.
Score: 3 Votes (Like | Disagree)

🔗 Related Apple News & Rumors

Stay updated with the latest Apple ecosystem news and verified rumors