Researcher Breaches Systems of Over 35 Companies, Including Apple, Microsoft, and PayPal - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Researcher Breaches Systems of Over 35 Companies, Including Apple, Microsoft, and PayPal

A security researcher was able to breach the internal systems of over 35 major companies, including Apple, Microsoft, and PayPal, using a software supply chain attack (via Bleeping Computer).
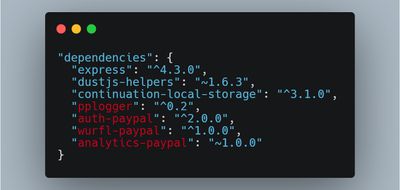
paypal hack

Security researcher Alex Birsan was able to exploit a unique design flaw in some open-source ecosystems called "dependency confusion" to attack the systems of companies such as Apple, Microsoft, PayPal, Shopify, Netflix, Yelp, Tesla, and Uber.

The attack involved uploading malware to open source repositories including PyPI, npm, and RubyGems, which were then automatically distributed downstream into the various companies' internal applications. Victims automatically received the malicious packages, with no social engineering or trojans required.

Birsan was able to create counterfeit projects using the same names on open-source repositories, each containing a disclaimer message, and found that applications would automatically pull public dependency packages, without needing any action from the developer. In some cases, such as with PyPI packages, any package with a higher version would be prioritized regardless of wherever it was located. This enabled Birsan to successfully attack the software supply chain of multiple companies.

Upon verifying that his component had successfully infiltrated the corporate network, Birsan reported his findings to the company in question, and some rewarded him with a bug bounty. Microsoft awarded him its highest bug bounty amount of $40,000 and released a white paper on this security issue, while Apple told BleepingComputer that Birsan will receive a reward via the Apple Security Bounty program for responsibly disclosing the issue. Birsan has now earned over $130,000 through bug bounty programs and pre-approved penetration testing arrangements.

A full explanation of the methodology behind the attack is available at Alex Birsan's Medium page.


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
deep black iphone 18 pro

Apple Says iPhone 18 Pro Max Sold in U.S. Differs in One Way

Saturday September 12, 2026 3:27 pm PDT by
As noted by Nicolas Lellouche, who writes for the French tech website Numerama, Apple has updated its tech specs pages for the iPhone 18 Pro and iPhone 18 Pro Max to clarify which models are equipped with its new C2 cellular modem and where. Apple now says the iPhone 18 Pro has a C2 modem worldwide, while the iPhone 18 Pro Max uses the chip in every country except for the U.S. According...

Top Rated Comments

hybrid_x Avatar
73 months ago
I love that ethical hackers can actually earn a decent income through bug bounty programs.
Score: 27 Votes (Like | Disagree)
73 months ago
Well played sir, well played!

I'm glad companies have bounty programs to encourage the "good guys" to report vulnerabilities. I have no idea how much time he put into the exploit but 130k is a nice payday.
Score: 16 Votes (Like | Disagree)
Stephen.R Avatar
73 months ago

People put too much trust in open-source community and software and this is the price they pay.
the irony of your statement is superb.

if the packages he spoofed had been open source he wouldn’t have been able to pull it off - it worked specifically because the companies were referencing internal/private packages (thus not open source) and he was able to make fake packages with the same name, in open source package repositories.

This type of shenanigans is just another reason why you should always vendor your dependencies kids.
Score: 12 Votes (Like | Disagree)
Kabeyun Avatar
73 months ago
This reminds me of the Russians hacking SolarWinds. Don’t get to the companies, get to the software the companies use and trust. Of course the irony is that these companies are some of the same ones that have been spending years trying to teach us not to automatically trust downloaded software.
Score: 11 Votes (Like | Disagree)
Blackstick Avatar
73 months ago
Well, time to hire this guy...
Score: 9 Votes (Like | Disagree)
73 months ago

People put too much trust in open-source community and software and this is the price they pay.

Open-source software, unless independently audited, have no guarantees of being secure (or even functional). Remember the disclaimer “this software is provided ‘AS IS’...”

They might even contain malicious code, since very few people will actually read the code before executing it.
The issue isn't open source - it's in the distribution model of software dependencies. This vulnerability has been known for quite some time.
Score: 7 Votes (Like | Disagree)

🔗 Related Apple News & Rumors

Stay updated with the latest Apple ecosystem news and verified rumors