Root Access Sudo Bug Found to Affect macOS Big Sur - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Root Access Sudo Bug Found to Affect macOS Big Sur

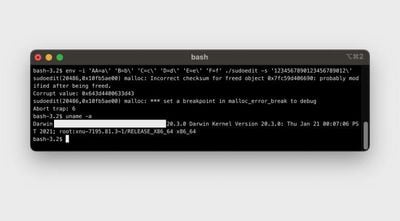
A sudo bug that can grant an attacker root access has been discovered to affect macOS Big Sur (via ZDNet).
sudo bug macos

The security vulnerability, identified last week as "CVE-2021-3156" by the Qualys Security Team, affects sudo, which is a program that allows users to run commands with the security privileges of another user, such as an administrator. The bug triggers a "heap overflow" in sudo that changes the current user's privileges to enable root-level access. This can give an attacker access to the entire system. An attacker would need to gain low-level access to a system first to be able to exploit the bug, such as via planted malware.

Sudo is part of many Unix-like systems, including macOS, but it was initially unknown if the vulnerability affected Mac machines since it was only tested by Qualys on Ubuntu, Debian, and Fedora. Security researcher Matthew Hickey has now confirmed that the most recent version of macOS, macOS Big Sur 11.2 can be subject to the sudo attack.

Last week, there was speculation that the macOS Big Sur 11.2 update may address the sudo vulnerability, though it was not definitively known at the time if the bug would affect macOS. While it was found that sudo was left unchanged in macOS Big Sur 11.2, it is now clear that macOS is affected by the exploit.

With some minor modifications, Hickey found that the sudo bug could be used to grant attackers access to macOS root accounts, and the discovery has now been verified by Carnegie Mellon University vulnerability analyst Will Dormann.

Apple has reportedly been notified of the CVE-2021-3156 vulnerability, and due to the severity of the issue, a patch will likely be released soon.


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

73 months ago

Apple rushing beta software to market, again.
This vulnerability has been present for more than a decade in all sorts of UNIXes! It's not something at all limited to Apple's QA...
Score: 34 Votes (Like | Disagree)
Havalo Avatar
73 months ago


Attachment Image
Score: 31 Votes (Like | Disagree)
73 months ago

So, mostly free OSes. That's much of a defense....

Devs knew about the potential, and chose not to address it. They would rather rush a beta product to market.
One day you will learn more about software and you will look back at this comment and say "wow, I was totally clueless back then."
Score: 27 Votes (Like | Disagree)
Gabebear Avatar
73 months ago

Wow I thought this would have been patched out in 11.2. Hopefully we will get a
supplemental patch shortly.
It turns most fairly minor security issues into full-blown root exploits… fairly terrifying.
Score: 9 Votes (Like | Disagree)
73 months ago

I'd think we'd have better tools/procedures for finding bugs like this a lot sooner.

Is there not an automated tool that can look at some code and say "hey, right here it's possible for a heap overflow to occur and there's no error handling code to deal with it"?
Sure there are tools that catch some of these problems via static analysis etc and there are languages where this class of problems might not even occur.

But it is also true that the day that the CVE was released I updated my Linux servers and got a fixed/patched sudo, while even macOS 11.3 beta1 still has the issue, so this is also indicative of Apple release engineering capabilities, or lack of them.
Score: 8 Votes (Like | Disagree)
justperry Avatar
73 months ago

So is this a zero day, drive-by vulnerability? Or does the attacker have to have physical access?
Nope

"An attacker would need to gain low-level access to a system first to be able to exploit the bug, such as via planted malware."
Score: 8 Votes (Like | Disagree)

🔗 Related Apple News & Rumors

Stay updated with the latest Apple ecosystem news and verified rumors