Apple Tells Congress 'Nothing Was Ever Found' to Suggest Alleged Supply Chain-Based Hack - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Apple Tells Congress 'Nothing Was Ever Found' to Suggest Alleged Supply Chain-Based Hack

Apple's top security chief told the U.S. Congress on Sunday that it had found no indication of suspicious transmissions or other evidence that its China supply chain was ever compromised (via Reuters).
the big hack bloomberg
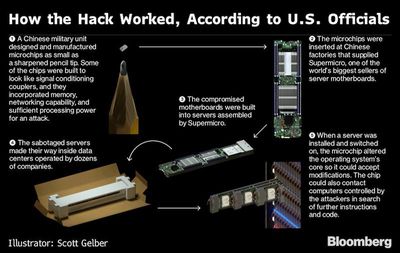
In a letter to the Senate and House commerce committees, Apple Vice President for Information Security George Stathakopoulos wrote that the company had repeatedly investigated and found no evidence to support Bloomberg Businessweek's bombshell report that alleged tiny chips were discovered inside Apple servers which allowed for backdoor transmissions to Chinese spies.

"Apple's proprietary security tools are continuously scanning for precisely this kind of outbound traffic, as it indicates the existence of malware or other malicious activity. Nothing was ever found," he wrote in the letter provided to Reuters.

Stathakopoulos repeated Apple's statements to the press that it had never found any such planted chips or been contacted by the FBI over the alleged matter. The letter follows a statement issued on Saturday by the U.S. Department of Homeland Security saying it had no reason to doubt the companies who denied that they had ever discovered the tiny chips.

Apple, Amazon, and Supermicro all strongly rebutted the report, which alleged that Chinese intelligence planted microchips in Supermicro servers, which Apple and Amazon previously used in their data centers.

Despite the denials, which are also backed by the UK's national cyber security agency, retired Apple general counsel Bruce Sewell, and other unnamed Apple senior executives, Bloomberg said it stood by its report as of Friday, but didn't immeditately respond to requests for comment on Sunday.

Note: Due to the political nature of the discussion regarding this topic, the discussion thread is located in our Politics, Religion, Social Issues forum. All forum members and site visitors are welcome to read and follow the thread, but posting is limited to forum members with at least 100 posts.
Popular Stories

iPhone Ultra Fold Feature

Foldable 'iPhone Ultra' May Launch Later in China, Says Leaker

Tuesday September 8, 2026 4:46 am PDT by
Apple's foldable "iPhone Ultra" may launch in mainland China later than in some other markets, according to an oft-reliable Chinese leaker. Posting on the Weibo social media platform, Instant Digital said that Apple has a limited initial inventory for its first foldable device, and the rollout could be shaped by regional allocation. The claim follows a recent report out of Japan...
iPhone 17 17 Pro and Air Feature

Smartphone Sales Are Falling Worldwide, But Apple Keeps Growing

Friday August 21, 2026 6:38 am PDT by
Apple gained ground in India, Latin America, and Europe even as all three markets contracted, according to a new series of Counterpoint Research reports. Between late March and the beginning of August, Indian smartphone sales ran 14% behind the equivalent stretch of 2025, and the market slipped for three straight weeks once major promotions in July had finished. Apple outperformed every...
iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...

Top Rated Comments

Scottsoapbox Avatar
104 months ago
There are many ways to mask communications. I'm not surprised they found nothing.
Name one undetectable by common practices.

Fortune 500 companies employ teams of IT security experts. So please enlighten us armchair hacker.
Score: 20 Votes (Like | Disagree)
BaltimoreMediaBlog Avatar
104 months ago
This is a Dog & Pony Show. If there's an ongoing investigation, #1, they rarely will even tell you. #2 Apple and others might not even know about it. It's even possible no one will ever know if its a vulnerability that is still existing and could be done again. The government never confirms stuff like this and strongly warns companies to do the same while secretly working behind the scenes. Everyone would be told to DENY ANYTHING. If we do find out anything, it will only be AFTER any possible issue is resolved, not during. Could be years!
Score: 18 Votes (Like | Disagree)
104 months ago
Bloomberg joining #fakenews now? Sad!
Score: 15 Votes (Like | Disagree)
Scottsoapbox Avatar
104 months ago
No serious hacker enters through the front door. Thinking outside the box is all the fun. I mentioned the LZ4 frame format above, but even SSH, generally considered secure, also has the potential for abuse (although admittedly it is more difficult). The initial key exchange initialization (called a kexinit packet) contains some fields that are, in my experience, usually ignored. The potential is there for abuse as well. Generally, communication originating internally is a much more difficult thing to contain, but it certainly isn't impossible.

:rolleyes: I'm actually Security+ certified, so maybe I know a little more than you do.
Wow a certification! How many *weeks* was the class for that? I mean the exam has 90 whole questions. :rolleyes:

You know some people get whole degrees from accredited universities in this stuff.

Again you didn't list an undetectable way to communicate massive data with China. You listed areas that "abuse" could occur. Malware doing something is one thing. Malware on thousands of servers transmitting back to the motherland without any notice of the outbound traffic is something completely different.
Score: 13 Votes (Like | Disagree)
AngerDanger Avatar
104 months ago
That diagram and entire article looks like something out of a 1993 Popular Mechanics magazine.
And from a quick glance, it looks like the illustrations depict china hacking our pencils!


Attachment Image
Score: 11 Votes (Like | Disagree)
Markoth Avatar
104 months ago
Wow a certification! How many *weeks* was the class for that? I mean the exam has 90 whole questions. :rolleyes:

You know some people get whole degrees from accredited universities in this stuff.

Again you didn't list an undetectable way to communicate massive data with China. You listed areas that "abuse" could occur. Malware doing something is one thing. Malware on thousands of servers transmitting back to the motherland without any notice of the outbound traffic is something completely different.
I have a degree from an accredited university, and I also have multiple certifications. I can send you the certs in an email if you're curious.

Insulting the Security+ makes you look foolish, so please continue.
Score: 11 Votes (Like | Disagree)

🔗 Related Apple News & Rumors

Stay updated with the latest Apple ecosystem news and verified rumors















