macOS High Sierra Vulnerability Allegedly Allows Malicious Third-Party Apps to Access Plaintext Keychain Data - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

macOS High Sierra Vulnerability Allegedly Allows Malicious Third-Party Apps to Access Plaintext Keychain Data

macOS High Sierra, released to the public today, could be impacted by a major security flaw that could allow a hacker to steal the usernames and passwords of accounts stored in Keychain.

As it turns out, unsigned apps on macOS High Sierra (and potentially earlier versions of macOS) can allegedly access the Keychain info and display plaintext usernames and passwords without a user's master password.

Security researcher and ex-NSA analyst Patrick Wardle tweeted about the vulnerability early this morning and shared a video of the exploit in action.


For this vulnerability to work, a user needs to download malicious third-party code from an unknown source, something Apple actively discourages with warnings about apps downloaded outside of the Mac App Store or from non-trusted developers. In fact, Apple does not even allow apps from non-trusted developers to be downloaded without explicitly overriding security settings.

As demonstrated in the video above, Wardle created a proof-of-concept app called "keychainStealer" that was able to access plaintext passwords stored in Keychain for Twitter, Facebook, and Bank of America. Wardle spoke to Forbes about the vulnerability and said it's actually not hard to get malicious code running on a Mac even with Apple's protections in place.
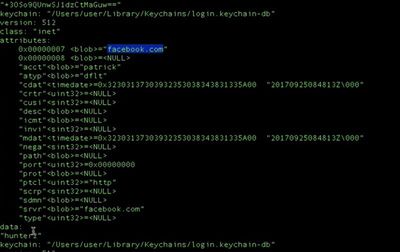
keychainpasswordexploit

"Without root priveleges, if the user is logged in, I can dump and exfiltrate the keychain, including plaintext passwords," Wardle told Forbes. "Normally you are not supposed to be able do that programmatically."

"Most attacks we see today involve social engineering and seem to be successful targeting Mac users," he added. "I'm not going to say the [keychain] exploit is elegant - but it does the job, doesn't require root and is 100% successful."

Wardle has not provided the full exploit code for malicious entities to take advantage of, and he believes Apple will patch the problem in a future update.

As Wardle has not released the full exploit code, it has not been double-checked by MacRumors or another source, so full details on the vulnerability are not known just yet.

Apple has not yet responded to requests for comment about the potential vulnerability.

Related Forum: macOS High Sierra

Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
deep black iphone 18 pro

Apple Says iPhone 18 Pro Max Sold in U.S. Differs in One Way

Saturday September 12, 2026 3:27 pm PDT by
As noted by Nicolas Lellouche, who writes for the French tech website Numerama, Apple has updated its tech specs pages for the iPhone 18 Pro and iPhone 18 Pro Max to clarify which models are equipped with its new C2 cellular modem and where. Apple now says the iPhone 18 Pro has a C2 modem worldwide, while the iPhone 18 Pro Max uses the chip in every country except for the U.S. According...

Top Rated Comments

117 months ago
Would have been great if he contacted Apple before the OS was released. Just looking for attention. Jerk
Score: 58 Votes (Like | Disagree)
117 months ago
Would have been great if he contacted Apple before the OS was released. Just looking for attention. Jerk
1. Would have been even greater if Apple had ppl who found these kind of bugs themselves before release.
2. You don't know if he found this yesterday. But sure hate on the guy who might have prevented your bank account password from ending up in the wrong hands.
Score: 52 Votes (Like | Disagree)
bladerunner2000 Avatar
117 months ago
On release day. That's embarrassing.
Score: 38 Votes (Like | Disagree)
carlsson Avatar
117 months ago
OMG, to enable this software you have to enter System Preferences, answer YES on two dialogues, and also enter your password. Then it may STEAL your not encoded things stored in the keychain (by default everything is stored encoded). I think I'm going to Windows now. This is just too much!!!

/irony ended
Score: 34 Votes (Like | Disagree)
s15119 Avatar
117 months ago
sigh. don't download junk, don't jeopardize your computer. Common sense is the best anti-virus.
Score: 21 Votes (Like | Disagree)
bladerunner2000 Avatar
117 months ago
If he did find it yesterday, he should have disclosed it to Apple and given them 90 days to fix it.
He doesn't owe Apple anything. Just like Apple doesn't owe him anything. He did them a favour.
Score: 19 Votes (Like | Disagree)

🔗 Related Apple News & Rumors

Stay updated with the latest Apple ecosystem news and verified rumors
















